Posted on — Leave a comment

Key Changes in ISO 9001:2026: Enhancing Quality Management Standards

The upcoming ISO 9001:2026 standard represents a significant evolution in Quality Management Systems (QMS). For certified organizations, understanding the impending changes is essential for maintaining compliance and enhancing operational efficacy. This transition requires careful planning, assessment, and adaptation. As the ISO community anticipates these updates, it is crucial for Quality Managers and ISO consultants to familiarize themselves with the implications of the new standard to ensure a smooth transition.

What Changes with ISO 9001:2026

ISO 9001:2026 is set to introduce several enhancements aimed at bolstering a systematic and risk-based approach to quality management. While many principles established in ISO 9001:2015 will remain intact, the focus will shift towards integrating advanced performance management and sustainability practices. Key areas of change are expected to include:

  • Enhanced Risk Management: Organizations will need to adopt a more proactive stance on risk assessment, emphasizing continual improvement through an integrated risk-based approach that aligns with company goals.
  • Incorporation of Technological Advancements: The standard may address the integration of digital technologies and data analytics within QMS, reflecting the ongoing digital transformation in industries worldwide.
  • Sustainability and Social Responsibility: A growing emphasis on sustainability metrics and social accountability will likely be a highlight, urging organizations to align their QMS with broader societal goals.

Differences from ISO 9001:2015

While maintaining foundational principles established in ISO 9001:2015, the transition to ISO 9001:2026 is expected to address several gaps and introduce refinements:

  • Terminology Updates: Clarifications in definitions and terms used throughout the standard to reduce ambiguities, making interpretation easier and more consistent.
  • Performance Evaluation: New metrics and ways of evaluating organizational performance may be introduced, focusing on long-term sustainability rather than short-term outputs.
  • Stakeholder Inclusivity: Greater emphasis on engaging stakeholders in the quality process, which may also require organizations to document stakeholder requirements transparently.

Impact on the Quality Management System

The implications of transitioning to ISO 9001:2026 will be profound. Organizations will need to evaluate their current QMS practices and align them with the new expectations of the standard. Key impacts include:

  • Process Review: Organizations may need to reassess major processes under the QMS to ensure they are capable of meeting new performance metrics and accountability requirements.
  • Documentation Adjustments: Enhanced documentation practices will be necessary to capture new processes and controls introduced under the revised standard, ensuring compliance and traceability.
  • Training and Culture Shift: A cultural shift towards sustainability, digital integration, and stakeholder management may require organizations to invest in training and development to equip their workforce with necessary skills.

Documents and Procedures to Review

Transitioning to ISO 9001:2026 will necessitate an extensive review of existing documents and processes. The focus should be on:

  • Quality Manual: Re-evaluate and possibly revise the Quality Manual to reflect new terminologies, processes, and strategic directions.
  • Procedures and Work Instructions: Update operating procedures and work instructions to incorporate changes in performance evaluations, risks, and stakeholder engagement.
  • Records Management: Ensure records of training, audits, and other QMS activities are updated to align with any new requirements related to documentation.

What Quality Managers Should Do

Quality Managers play a crucial role in facilitating the transition to ISO 9001:2026. Here are practical steps they should consider:

  • Conduct a Gap Analysis: Perform a thorough ISO 9001 Gap Analysis to identify areas of non-compliance or required enhancements between the current state under ISO 9001:2015 and expectations of ISO 9001:2026.
  • Engage Stakeholders: Open dialogues with stakeholders to better understand their needs and how they can be integrated into the QMS.
  • Training and Development: Prepare training programs aimed at helping staff understand new practices, technologies, and metrics introduced in the ISO 9001:2026.

How to Prepare for the Transition

Preparations for the move to ISO 9001:2026 should be strategic and systematic. Organizations can employ the following methods to ensure readiness:

  • Establish a Transition Team: Form a dedicated team to oversee the transition process, ensuring it includes cross-functional representation from various departments.
  • Update Internal Audit Plans: Revise internal audit plans to include assessments of new processes, controls, and performance indicators introduced in ISO 9001:2026.
  • Communicate Changes Effectively: Develop a communication plan that outlines changes and timelines, ensuring transparency throughout the organization.

How to Prepare for ISO 9001:2026

The transition from ISO 9001:2015 to ISO 9001:2026 is significant and requires proactive measures to ensure compliance and operational effectiveness. Conducting a Gap Analysis in advance can reveal areas requiring attention and adjustment. Furthermore, a comprehensive review of the Quality Manual, existing procedures, forms, internal audits, and overall QMS documentation is essential to align with the new standard’s requirements seamlessly.

By preparing now, organizations can not only comply with the updated standard but also leverage these changes to enhance their overall quality management practices, driving both improvement and competitive differentiation in their respective markets.

Posted on — Leave a comment

Empowering Consultants in Regulatory Frameworks

Introduction

The EU NIS 2 Directive, a significant amendment to the existing Directive on Security of Network and Information Systems (NIS), was established to enhance the cybersecurity posture across the European Union. Enacted in December 2020, it reflects the EU’s commitment to strengthening cybersecurity defenses in an increasingly interconnected digital economy. The objectives of NIS 2 encompass improving the overall cybersecurity resilience of essential and important entities across member states, setting higher common security standards, and enhancing cooperation among national authorities.

The directive applies to a wide variety of sectors, including energy, transport, health, and digital infrastructure, expanding the framework to cover more organizations than its predecessor. With this shift, organizations must grapple with practical implications such as compliance deadlines, incident reporting requirements, and establishing stronger security measures to minimize risks.

Cybersecurity Risk Management Obligations

One focal area of the NIS 2 Directive is the establishment of robust cybersecurity risk management obligations. The directive mandates that organizations develop, implement, and maintain comprehensive policies addressing cybersecurity risks. This includes assessing potential threats and vulnerabilities, as well as implementing appropriate technical and organizational measures.

Operational Impacts and Compliance Challenges

For organizations striving for compliance, the operational implications are profound. Establishing a risk management framework involves not only understanding and addressing potential cyber threats but also aligning organizational practices to meet specific regulatory requirements. Many companies may face challenges such as:

  • Resource Allocation: Companies often struggle with allocating sufficient resources, both in terms of budget and personnel, to develop and maintain an effective cybersecurity risk management framework.

  • Integration of Security Practices: Implementing cybersecurity measures within existing processes and workflows can lead to operational disruptions. Organizations must find a balance between compliance and operational efficiency.

Common Gaps and Regulatory Expectations

An area of concern for many organizations is the common gaps in compliance. Often, organizations fail to adequately address issues such as:

  • Lack of Continuous Risk Assessment: Many organizations adopt a one-time assessment approach, failing to realize that cybersecurity threats are continuously evolving and require ongoing evaluation.

  • Insufficient Training and Awareness: Employees play a crucial role in cybersecurity. Organizations must ensure that staff are adequately trained and aware of cybersecurity practices to mitigate risks effectively.

Practical Compliance Section

Organizations seeking to comply with the NIS 2 Directive must take several concrete steps:

Required Policies and Procedures

  1. Develop a Cybersecurity Policy: Establish a comprehensive cybersecurity policy that emphasizes risk management, incident response, and continuous improvement.

  2. Conduct Regular Risk Assessments: Implement a framework for regular risk assessments that identify vulnerabilities and threats.

Evidence Documentation

During audits or inspections, organizations should prepare to present various forms of evidence, including:

  • Risk Assessment Reports: Detailed reports outlining how risks were assessed, the methodology used, and the identified vulnerabilities.

  • Incident Response Plans: Documentation illustrating the procedures in place for incident detection, reporting, containment, and recovery.

Best Practices for Ongoing Compliance

To demonstrate ongoing compliance and commitment to cybersecurity, organizations can adopt the following best practices:

  • Security Awareness Training: Conduct regular training sessions to ensure all employees understand cybersecurity policies and their roles in maintaining security.

  • Consistency in Reporting: Establish a consistent reporting protocol for security incidents to ensure timely communication with relevant authorities.

Conclusion

In summary, the EU NIS 2 Directive represents a leap forward in enhancing the cybersecurity landscape across Europe. By focusing on stringent risk management obligations, the directive requires organizations to take a proactive stance in their cybersecurity practices. Continuous compliance with NIS 2 not only supports the organization’s cybersecurity posture but also fosters trust among clients and partners.

Given the evolving nature of cyber threats, a structured and continuous approach to NIS 2 compliance will be essential for organizations aiming for resilience in today’s digital economy. By aligning their practices with regulatory requirements, businesses can not only secure their operations but contribute to a more secure and trustworthy digital ecosystem in the European Union.

Posted on — Leave a comment

ISO 9001:2026 Key Updates for Quality Managers and ISO Consultants

The looming changes brought forth by the ISO 9001:2026 standard signify a pivotal moment for organizations currently certified under ISO 9001:2015. It is crucial for Quality Managers, ISO consultants, and auditors to comprehend these changes to ensure a seamless transition and continued compliance. This article provides a comprehensive overview of what organizations can expect as they prepare for ISO 9001:2026.

What Changes with ISO 9001:2026

ISO 9001:2026 represents an evolution of the quality management system framework established in ISO 9001:2015. While specific details of the finalized standard are still pending, several key themes are anticipated based on the current drafts and discussions within ISO working groups.

Emphasis on Risk-based Thinking

One of the most significant anticipated changes in ISO 9001:2026 is the enhanced focus on risk-based thinking. While ISO 9001:2015 introduced this concept, ISO 9001:2026 is expected to deepen its integration into organizational processes and QMS activities.

Greater Alignment with Digital Transformation

As organizations increasingly embrace digital technologies, the new standard will likely reflect increased emphasis on integrating digital tools into quality management processes. This may involve requirements for data analysis and the effective use of digital documentation and communication systems.

Differences from ISO 9001:2015

Understanding the differences between ISO 9001:2015 and ISO 9001:2026 is imperative for effective transition planning.

Structure and Language Refinement

The structure of the standard may see revisions to clarify requirements, ensuring consistency between ISO 9001:2026 and other management system standards. This might include updates to terminology that enhance understanding across diverse industries.

Anticipated Inclusion of Sustainability Principles

There is a strong possibility that ISO 9001:2026 will incorporate more explicit guidelines surrounding sustainability practices, encouraging organizations to consider their environmental and social responsibilities within their quality management frameworks.

Impact on the Quality Management System

Organizations currently certified under ISO 9001:2015 will need to assess how the upcoming changes impact their existing Quality Management Systems (QMS).

Integration with Business Strategy

As risk-based thinking and digital transformation take precedence, companies ought to align their QMS with strategic objectives. This means that quality management should play an integral role in overall business goals, influencing decision-making processes across all levels.

Enhancement of Stakeholder Engagement

ISO 9001:2026 is likely to put increased focus on stakeholder engagement, necessitating that organizations re-evaluate how they communicate and interact with customers, employees, and other stakeholders to enhance satisfaction and trust.

Documents and Procedures to Review

For organizations preparing for the transition, several documents and procedures will require thorough review and potential updates.

Key Documentation to Focus On

  • Quality Manual: Ensure alignment with new requirements, including any updates in policy statements.
  • Procedures and Work Instructions: Review processes for effectiveness and efficiency in light of the anticipated changes in risk management protocols.
  • Internal Audit Procedures: Adapt internal audit methodologies to address new areas of focus, especially concerning digital data analysis and stakeholder engagement.
  • Risk Management Documentation: Revise your risk assessment processes to incorporate deeper risk-based thinking strategies as expected in ISO 9001:2026.

Quality Metrics

Organizations should review their quality metrics to assess how well they align with the possible updates related to operational performance and stakeholder satisfaction metrics.

What Quality Managers Should Do

Quality Managers have a pivotal role in preparing for the transition to ISO 9001:2026. Here are some practical steps they can take:

Conduct a Gap Analysis

A Gap Analysis should be the first step in assessing how the organization’s current QMS aligns with forthcoming ISO 9001:2026 requirements. This analysis will identify areas of non-compliance and inform the development of a transition strategy.

Engage Stakeholders Early

Involving key stakeholders early in the transition process is crucial. Their input can provide valuable insights into necessary adjustments and foster a culture of inclusivity around quality management.

Train Staff on New Concepts

As the standard evolves, so too should the knowledge base of staff. Implement training sessions focused on the new concepts in the standard, particularly regarding risk-based thinking and sustainability.

How to Prepare for the Transition

To effectively prepare for the changes associated with ISO 9001:2026, organizations can adopt the following strategies:

Develop a Transition Plan

Creating a structured transition plan that includes timelines, responsible individuals, and milestones will facilitate a smoother shift to ISO 9001:2026.

Continuous Monitoring and Improvement

Organizations should foster a culture of continuous improvement. Regularly review quality management processes and document any findings as a basis for ongoing enhancement.

Stakeholder Communication Strategy

Establish a communication plan that ensures all stakeholders are kept informed about the transition process, involved in discussions, and aware of any changes that affect them.

How to Prepare for ISO 9001:2026

Transitioning from ISO 9001:2015 to ISO 9001:2026 is a comprehensive endeavor that requires careful planning and execution. Organizations should conduct a Gap Analysis well in advance, focusing on reviewing the Quality Manual, procedures, forms, internal audits, and other QMS documentation.

By embracing the anticipated changes proactively and rigorously assessing existing systems, organizations can not only achieve compliance with ISO 9001:2026 but also enhance their overall quality management practices.

Posted on — Leave a comment

NIS 2 – Elevating Cybersecurity Compliance for Organizations

Introduction

The EU NIS 2 Directive (Directive on Security of Network and Information Systems) serves as a pivotal piece of legislation aimed at increasing the cybersecurity resilience of entities across the European Union. As a successor to the original NIS Directive, NIS 2 broadens its scope to cover a more extensive range of sectors and introduces more stringent requirements that organizations must adhere to. The primary objective of the directive is to enhance cybersecurity practices across EU member states and to ensure a unified approach to managing cyber risks.

The NIS 2 Directive applies to essential and important entities across crucial sectors such as energy, transport, health, and digital infrastructure. Organizations, including both public and private entities, are expected to implement risk management measures, report significant incidents, and enhance overall cybersecurity resilience. This regulatory framework poses practical implications for organizations, making compliance not just a legal obligation but a necessity for maintaining operational integrity and protecting critical services.

Focus Topic: Cybersecurity Risk Management Obligations

Understanding Risk Management Obligations under NIS 2

One of the primary focal points of the NIS 2 Directive is the stringent cybersecurity risk management obligations imposed on organizations. NIS 2 emphasizes the need for a robust culture of risk management that permeates all levels of the organization. This includes not only the deployment of technical security measures but also the fostering of an organizational ethos that prioritizes cybersecurity.

Under NIS 2, organizations are required to conduct comprehensive risk assessments to identify potential vulnerabilities and threat vectors. This risk assessment process must be ongoing and adaptive, with organizations regularly updating their risk management practices to reflect changes in their operating environment and the threat landscape.

Operational Impacts and Compliance Challenges

Implementing the comprehensive risk management obligations set forth by NIS 2 presents a multitude of operational impacts and compliance challenges. Organizations must ensure that they have the necessary resources, expertise, and tools in place to conduct thorough risk assessments, which may necessitate investment in new technologies and personnel training. Furthermore, varying levels of maturity across different sectors may lead to inconsistent compliance efforts, making it crucial for organizations to benchmark against best practices.

Common gaps that organizations may encounter include the lack of a formalized risk management strategy, insufficient documentation of assessments, and inadequate integration of cybersecurity practices into broader organizational strategies. The regulatory expectations are clear: organizations must not only have mechanisms in place for risk management but also must be able to demonstrate their effectiveness and compliance through documentation and reporting.

Practical Compliance Section

Concrete Steps for Compliance

To align with the NIS 2 requirements, organizations should take the following steps:

  1. Conduct a Comprehensive Risk Assessment: Identify and evaluate risks specific to your organizational context including physical, personnel, and technology reserves.

  2. Develop Risk Management Policies: Create and document policies that reflect your organization’s approach to managing cyber risks. Include guidelines for regular updates and reviews.

  3. Implement Technical and Organizational Measures: Create a multilayered security architecture that encompasses preventive, detective, and corrective controls. This includes firewalls, access control mechanisms, and employee cybersecurity training.

  4. Establish Incident Response Procedures: Develop clear protocols for managing and reporting cybersecurity incidents, ensuring that employees know how to act in the face of an incident.

  5. Foster a Cybersecurity Culture: Promote awareness and training programs to instill a culture of cybersecurity resilience throughout the organization.

Required Documentation for Audits

During audits or inspections, organizations can expect to provide the following documentation:

  • Evidence of completed risk assessments and resultant risk management strategies.
  • Records of incidents, including notifications to relevant authorities and follow-up actions taken.
  • Documentation of policies and procedures related to cybersecurity governance.
  • Training logs demonstrating workforce engagement in cybersecurity practices.

Best Practices for Ongoing Compliance

To demonstrate an ongoing commitment to compliance with NIS 2, organizations should:

  • Engage in periodic reviews of their cybersecurity policies and procedures, adapting them as necessary in response to changing circumstances and threats.
  • Implement continuous training and development sessions focused on cybersecurity awareness for all employees.
  • Maintain open lines of communication with regulatory bodies and industry peers to stay abreast of best practices and emerging threats.

Conclusion

The EU NIS 2 Directive presents both a challenge and an opportunity for organizations operating within its scope. By understanding and implementing the cybersecurity risk management obligations, organizations are not only complying with regulatory requirements but also cultivating a culture of resilience and trust with stakeholders. A structured and continuous approach to NIS 2 compliance is essential, ensuring that organizations can navigate the evolving landscape of cybersecurity threats while protecting their vital services and infrastructure. Embracing these measures ultimately strengthens the collective cybersecurity posture of the EU, benefiting all entities and citizens alike.

Posted on — Leave a comment

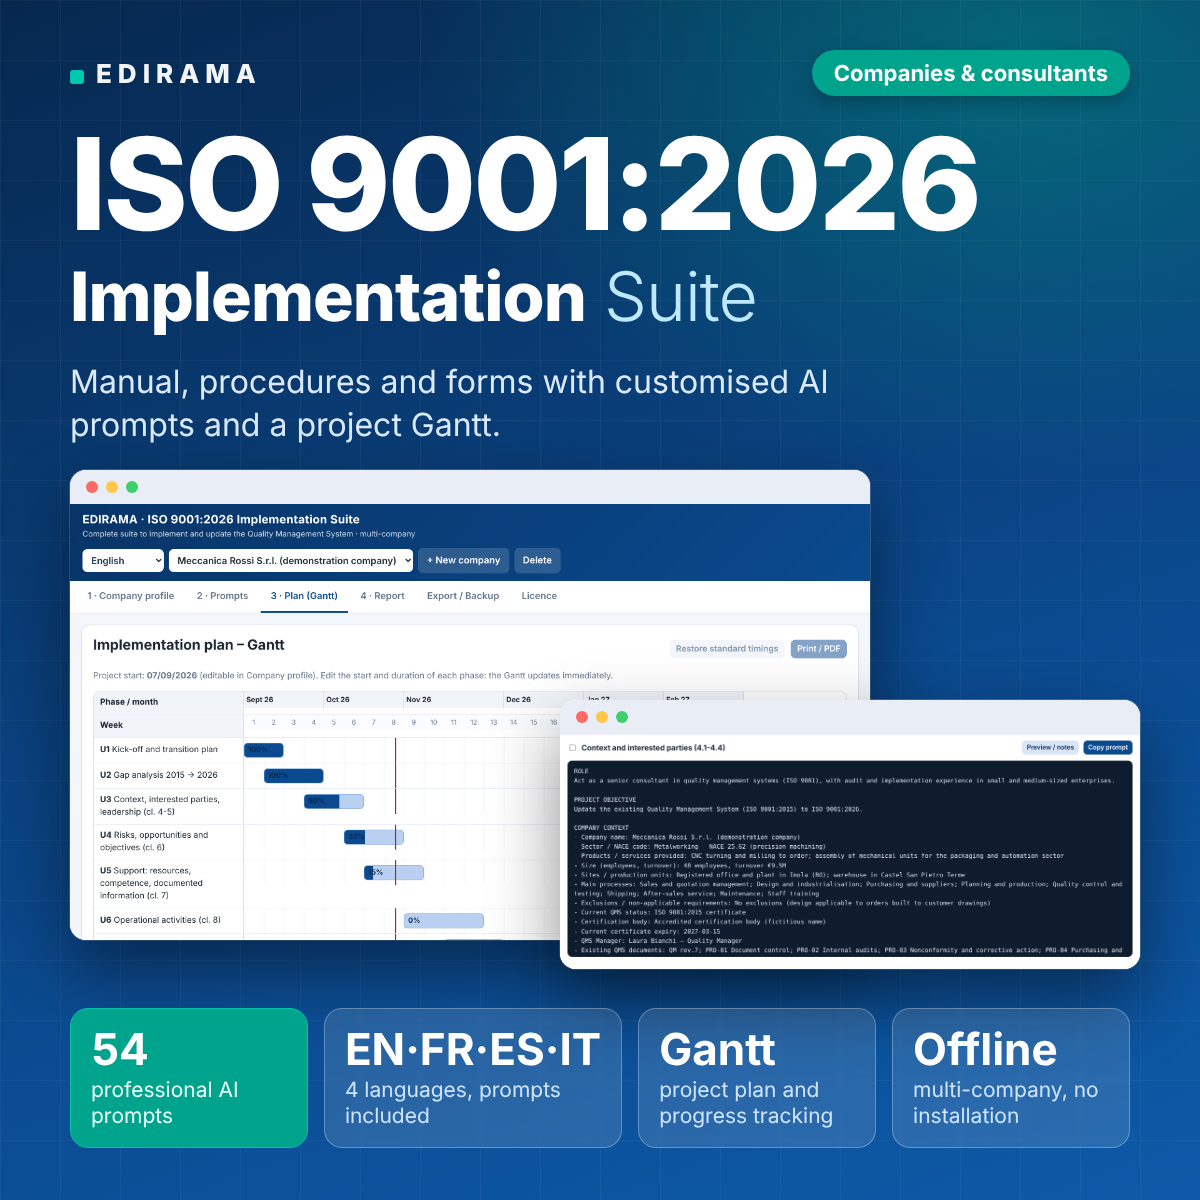
New ISO 9001 – ISO 9001:2026 Implementation Suite –

Updating or establishing a quality management system (QMS) to comply with the ISO 9001:2026 standard presents a significant challenge for many organizations. The process requires creating a comprehensive set of consistent documents such as manuals, procedures, work instructions, and forms, all aligned with the company’s real data and operational context. Without structured guidance, this task can be overwhelming, especially when managing multiple updates or clients.

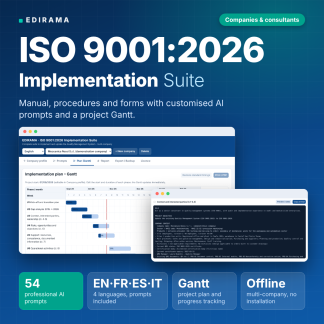
The ISO 9001:2026 Implementation Suite addresses this need by providing a guided, methodical approach to build or update a QMS efficiently. It is designed for two primary user groups: companies managing their own quality systems and consultants overseeing several clients. Whether updating an existing ISO 9001:2015 system or developing a new documentation system, the suite aids in maintaining organizational control and consistency throughout the project.

The suite includes:

  • Fifty-four professional, customizable prompts pre-filled with your company’s specific data, ensuring that generated documents are relevant and tailored.
  • A project Gantt chart that visualizes each phase with editable start dates and durations, tracking progress and helping users stay on schedule.
  • Language options supporting English, French, Spanish, and Italian, with the ability to switch languages anytime to accommodate international or multi-lingual environments.
  • Functionality to work offline directly in the browser, requiring no installation, cloud subscription, or external platform.
  • Export options including Excel for data, and PDF or print-friendly versions of reports, plans, and prompt libraries.

To utilize the suite, users begin by selecting their language and filling in a detailed company profile, including sector, processes, existing documentation, and key issues. Choosing between updating a 2015-certified system or creating a new system triggers the generation of a relevant phased plan. Users then copy prompts into their preferred AI assistant, inputting the official ISO text or company-specific details for accurate, compliant documentation. Progress is tracked through prompt completion, with updated reports ready for management or clients.

For companies, this tool provides autonomy in managing ISO 9001:2026 projects without reliance on full-time consultants, ensuring documents reflect real operational conditions and facilitating clear communication with leadership. Consultants benefit from centralized management of multiple client projects within one tool, promoting consistency across assignments and allowing more time for advisory activities rather than drafting foundational documents.

Overall, the ISO 9001:2026 Implementation Suite offers a structured, language-flexible, and offline-capable resource for organizations and consultants working toward ISO 9001:2026 compliance, helping manage the complexity and volume of work with clarity and efficiency.

Learn more about the contents and features: view the complete product page.

Posted on — Leave a comment

Navigating the Key Changes in ISO 9001:2026 for Quality Management Systems

ISO 9001:2026: Transitioning Towards Enhanced Quality Management Standards

The evolution of ISO 9001:2026 stands as a significant milestone for organizations seeking to improve their quality management systems (QMS). With ongoing advancements in quality practices and increased emphasis on organizational effectiveness, adapting to these updates is crucial for maintaining certification and competitive advantage in today’s dynamic market.

What Changes with ISO 9001:2026

While the final details of ISO 9001:2026 have yet to be fully articulated, several key changes are anticipated that build upon the foundation laid by ISO 9001:2015. The focus on organization-wide engagement, increased flexibility, and digital transformation presence will likely be stronger in this new version. Here are some expected updates:

  • Increased Emphasis on Context: There’s likely to be a greater emphasis on understanding the organization’s context, focusing on external and internal factors that influence QMS effectiveness.

  • Sustainability Integration: The integration of sustainability principles may become more explicit, aligning the quality management framework with broader organizational goals related to environmental and social impact.

  • Risk-Based Thinking: Though risk-based thinking was a cornerstone of ISO 9001:2015, ISO 9001:2026 may elevate this approach, mandating more thorough processes for identifying and mitigating risks.

Differences from ISO 9001:2015

While organizations may feel comfortable with their current ISO 9001:2015 setups, it is essential to recognize the distinctions that ISO 9001:2026 will likely introduce:

  • Greater Flexibility: The new standard is expected to offer more customizable pathways for organizations, allowing them to adapt QMS processes that best fit their unique operations.

  • Enhanced Stakeholder Engagement: Expect a shift towards more inclusive stakeholder engagement strategies that reflect customer and workforce feedback more prominently in the quality processes.

  • Digital Transformation: There may be increased requirements for leveraging data analytics and technology within QMS, encouraging organizations to adopt innovative solutions for quality assurance.

Impact on the Quality Management System

Transitioning to the new ISO 9001:2026 standard will undoubtedly affect various elements of an organization’s QMS. Here are the primary areas to focus on:

  • Policies and Objectives: Organizations will need to review their quality policies and objectives to ensure they align with the enhanced requirements for stakeholder consideration and sustainability.

  • Processes and Procedures: Processes should be revisited to prioritize both existing processes and any new workflows introduced by technological advancements and digitization.

  • Internal Audits and Compliance Checks: The internal audit methodologies may need revisions to effectively evaluate newly adopted practices and compliance with the updated criteria.

Documents and Procedures to Review

As part of the transition planning, organizations should focus on several critical documents and procedures:

  • Quality Manual: Review the entirety of the Quality Manual to ensure it captures the updated approach towards context, risks, and expectations under ISO 9001:2026.

  • Standard Operating Procedures (SOPs): Each SOP should be analyzed for relevance to new processes, risk assessments, and stakeholder feedback mechanisms.

  • Forms and Records: All relevant forms, templates, and records related to quality activities should be updated to reflect any changes in requirements or processes.

What Quality Managers Should Do

Quality Managers play a vital role in preparing for the transition to ISO 9001:2026. Here are actionable steps they should follow:

  • Conduct a Gap Analysis: Start with a comprehensive ISO 9001 Gap Analysis comparing the current QMS against the anticipated requirements of ISO 9001:2026. This analysis will highlight areas needing adjustment.

  • Engage Stakeholders: Initiate conversations with key stakeholders to surface insights and expectations that may influence quality objectives and policies moving forward.

  • Training and Capability Building: Organize training sessions for staff to familiarize them with the upcoming changes and to enhance capabilities in areas such as risk management and sustainability practices.

How to Prepare for the Transition

Preparing for the transition to ISO 9001:2026 involves multiple strategies and proactive measures. Companies should consider the following:

  • Review and Update Documentation: As outlined above, ensuring all QMS documentation is pertinent and compliant with new standards is critical.

  • Internal Audits: Schedule and conduct internal audits to assess and ensure compliance with both existing and anticipated practices, identifying non-conformities ahead of formal assessments.

  • Enhance Communication: Maintain open channels of communication within the organization, emphasizing the importance of the transition and fostering collaborative efforts across departments.

How to Prepare for ISO 9001:2026

Emphasizing the approach taken to prepare for ISO 9001:2026 is paramount. Organizations must implement an effective strategy to tackle the transition:

  1. Conduct a Thorough Gap Analysis: Identify gaps between current practices and those anticipated under ISO 9001:2026, using the analysis as a roadmap for required updates.

  2. Assess the Quality Manual and Associated Documentation: Scrutinize and revise the Quality Manual to ensure it reflects the new organizational focuses and adheres to upcoming standards.

  3. Prepare for Enhanced Audits: Develop an audit schedule that not only checks compliance with ISO 9001:2026 but also enhances internal awareness around quality culture and practices.

In conclusion, while the transition to ISO 9001:2026 presents challenges, it also offers opportunities for organizations to enhance their quality management frameworks. Conducting a timely Gap Analysis and thoroughly reviewing the Quality Manual, procedures, forms, and overall QMS documentation will be essential for a successful transition. Embracing these changes proactively will ensure firms not only remain compliant but thrive in delivering quality and stakeholder satisfaction.

Posted on — Leave a comment

NIS 2 – Strengthening Cyber Resilience and Compliance Strategies

Introduction

The European Union Network and Information Systems (NIS) 2 Directive represents a crucial regulatory framework intended to bolster the cybersecurity resilience of essential and important entities across Europe. Released in December 2020 and expected to be implemented by member states, the NIS 2 Directive aims to enhance the overall security standards of network and information systems while promoting better cooperation and information sharing among EU countries.

The primary objectives of the NIS 2 Directive include improving cybersecurity risk management policies, incident response capabilities, and supervisory mechanisms for essential services providers, encompassing energy, transport, banking, health, digital infrastructure, and the supply chain. Essentially, the directive mandates a higher level of accountability and resilience, compelling organizations to reassess and strengthen their cybersecurity posture.

For organizations falling under the directive’s scope, compliance is not just a regulatory requirement; it’s a vital component of operational integrity and public trust. Failure to adhere to NIS 2 can result in significant penalties, operational disruptions, and reputational damage.

Cybersecurity Risk Management Obligations under NIS 2

One of the hallmark features of the NIS 2 Directive is its emphasis on comprehensive cybersecurity risk management obligations. Under NIS 2, essential and important entities must adopt a risk-based approach to manage the cybersecurity risks they face. This section explores the operational impacts and compliance challenges associated with these obligations.

Understanding Risk Management Obligations

Organizations are required to implement appropriate technical and organizational measures to manage cybersecurity risks effectively. These measures must be proportional to the risks and the impact of possible incidents on the continuity of essential services. This includes identifying potential threats, vulnerabilities, and the potential consequences of incidents.

Operational Impacts and Compliance Challenges

Organizations might face various challenges in fulfilling these risk management obligations. For instance, the need to continually assess evolving threat landscapes can drain resources and demand specialized expertise. In addition, creating a comprehensive risk management strategy involves integrating cybersecurity across all operational areas and ensuring that all teams, from IT to executive management, understand their roles in maintaining security.

Common compliance challenges include:

  • Lack of clarity on specific risk management frameworks or standards to follow.
  • Inadequate resource allocation, both in terms of budget and human capital.
  • Difficulty in ensuring alignment with existing national legislation and directives.

Regulatory Expectations

The directive expects organizations to move beyond basic compliance checkboxes and adopt a culture of cybersecurity. The European Union Agency for Cybersecurity (ENISA) also provides guidance on best practices, emphasizing not just compliance but overall improvement in security maturity.

Practical Compliance Steps

Organizations must take concrete steps to ensure compliance with the NIS 2 Directive’s risk management obligations. Below are recommended actions and best practices.

Required Policies and Procedures

  1. Conduct a Cybersecurity Risk Assessment: Regularly evaluate risks to identify vulnerabilities and threats specific to your organization’s operations.

  2. Develop a Risk Management Policy: Draft a formal policy outlining the organization’s approach to managing cybersecurity risks. This should include defined roles and responsibilities.

  3. Implement Technical Security Measures: Establish firewalls, intrusion detection systems, and encryption protocols tailored to your organization’s needs.

  4. Operational Security Procedures: Document standard operating procedures (SOPs) for cybersecurity incidents, including response and recovery plans.

Documentation Expectations for Audits

To demonstrate compliance during audits or inspections, organizations should maintain accurate records, including:

  • Risk assessment documentation
  • Security policy and procedure manuals
  • Training records concerning cybersecurity awareness for staff
  • Incident response plans and documentation of handled incidents

Best Practices for Ongoing Compliance

  • Continuous Monitoring: Implement a continuous improvement process that regularly evaluates and enhances security measures.
  • Regular Training: Provide ongoing training for staff to keep them informed about threats and the importance of cybersecurity.
  • Engage with Stakeholders: Develop relationships with other organizations and regulators to share information on threats and best practices.

Conclusion

The EU NIS 2 Directive presents a significant shift in regulatory expectations for cybersecurity practices within essential and important entities. By emphasizing robust risk management obligations and operational accountability, the directive not only aims to improve resilience against cyber threats but also encourages a culture of continuous improvement and collaboration.

Successfully navigating these requirements will require organizations to take proactive steps in establishing a structured and ongoing compliance approach, ensuring their defenses remain resilient and effective in an ever-changing threat landscape. As such, organizations must view compliance not as a burden, but as an opportunity to enhance their overall cybersecurity posture and safeguard their operations for the future.

Posted on — Leave a comment

ISO 9001:2026 Insights: Key Changes Impacting Quality Management Systems

The upcoming transition to ISO 9001:2026 marks a significant step forward for organizations committed to enhancing their Quality Management Systems (QMS). Understanding the implications of this new standard is critical, as it will impact existing practices, documentation, and overall quality assurance efforts. Organizations currently certified under ISO 9001:2015 should proactively prepare for these changes to maintain compliance and improve their competitive advantage.

What Changes with ISO 9001:2026

ISO 9001:2026 is expected to introduce several modifications aimed at refining the principles of quality management. While the finalized text is yet to be published, anticipated updates focus on enhanced clarity in requirements, increased flexibility, and a stronger emphasis on stakeholder engagement and risk management.

Key Themes for Change

  • Greater Emphasis on Context: Organizations may face strengthened requirements around understanding external and internal factors that affect their QMS.
  • Risk Management Upgrades: There may be an expanded focus on integrating risk management into the core processes of the QMS, underlining the need for robust risk identification and assessment.
  • Stakeholder Involvement: Increased attention may be directed to stakeholder satisfaction and engagement, ensuring that organizations align their processes with stakeholder needs.

Differences from ISO 9001:2015

Although similarities between ISO 9001:2015 and the upcoming ISO 9001:2026 will remain, distinguishing between these versions is crucial for effective transition.

Key Differences

  • Terminology and Structure: The organizational context may receive a redefined structure and terminology to promote deeper understanding.
  • Process Thinking: There may be a push towards more explicit documentation of process interactions, encouraging an interconnected approach to quality management.
  • Documentation Flexibility: Expectations regarding documented information may evolve, with a potential relaxation in strict requirements in favor of a more tailored approach.

Impact on the Quality Management System

With these changes, organizations must evaluate how their QMS aligns with ISO 9001:2026. The transition process will likely require a thorough review of existing practices, ensuring that systems are compliant with new standards.

Implications for Existing Systems

  • Alignment with Stakeholders: Organizations will need to assess how well they currently engage and involve stakeholders in their quality management practices.
  • Integrating Risk Management: The focus will likely shift towards anticipating and mitigating risks in a more systematic manner, requiring the integration of risk assessments within existing QMS activities.
  • Documentation Review and Update: As a result of potential changes in documentation requirements, organizations may need to revisit their Quality Manuals, procedures, and forms.

Documents and Procedures to Review

The transition offers an opportunity for organizations to critically assess their current quality documentation. Focused evaluations should encompass:

  • Quality Manual: Review for alignment with new requirements.
  • Procedures: Ensure procedures reflect changes in terminology and expectations around stakeholder engagement.
  • Risk Management Plans: Adapt risk management processes according to anticipated updates in ISO 9001:2026.
  • Internal Audits: Assess whether internal audit procedures fully cover the updated requirements and emphasize the effectiveness of the QMS.

What Quality Managers Should Do

Quality Managers play a pivotal role in guiding their organizations through the transition to ISO 9001:2026. Here are practical steps to follow:

  1. Conduct a Gap Analysis: Evaluate the current QMS against potential requirements in ISO 9001:2026. Identify areas needing improvement or alignment.
  2. Engage Stakeholders: Involve relevant stakeholders in discussions to comprehend their needs and expectations, ensuring that the QMS adapts accordingly.
  3. Update Training Programs: Provide resources and training to staff on the anticipated changes to ensure understanding and compliance.
  4. Review and Adapt Documentation: Perform a comprehensive review of all documentation to align with the new standard’s requirements.

How to Prepare for the Transition

Preparation for ISO 9001:2026 requires a structured approach to ensure compliance and efficiency. Organizations should consider the following strategies:

  • Develop a Transition Plan: Outline a detailed plan that includes timelines, responsibilities, and measurable targets for attaining compliance.
  • Regular Communication: Keep all stakeholders informed about changes, progress, and expectations regarding the transition.
  • Pilot Tests: Conduct trials of new procedures or processes before full implementation, which helps identify potential issues.
  • Ongoing Monitoring: Establish metrics to evaluate the effectiveness of the new QMS elements and ensure continuous improvement.

Conclusion

The transition to ISO 9001:2026 presents an opportunity for organizations to enhance their quality management practices significantly. Undertaking a thorough Gap Analysis and revisiting the Quality Manual, procedures, forms, and internal audit strategies is essential to effectively align with the new standard. By anticipating changes and preparing comprehensively, organizations can ensure a seamless transition and continue to drive quality excellence.


Posted on — Leave a comment

Navigating NIS 2 Requirements for Decision-Makers

Introduction

The EU NIS 2 Directive marks a significant evolution in Europe’s approach to cybersecurity legislation, aimed at enhancing the overall cybersecurity posture across member states. Building upon its predecessor, the original NIS Directive, NIS 2 establishes more rigorous requirements aimed at improving resilience against cyber threats for a wide array of sectors, including essential services and digital infrastructure.

The objectives of NIS 2 are twofold: to enhance cybersecurity preparedness across Europe by enforcing a greater emphasis on risk management and incident reporting, and to foster cooperation and information sharing among member states to tackle the growing landscape of cyber threats. Its implications extend to a diverse range of organizations that fall under its scope, necessitating a proactive approach to compliance.

Cybersecurity Risk Management Obligations Under NIS 2

One of the core components of NIS 2 is the obligation for organizations designated as essential and important entities to implement comprehensive cybersecurity risk management practices. This section delves deeper into the operational impacts and compliance challenges that organizations face in fulfilling these obligations.

Understanding the Risk Management Framework

NIS 2 requires organizations to maintain a risk management framework that incorporates:

  • Risk Identification: Organizations must regularly assess potential threats and vulnerabilities that could impact their operations.
  • Risk Assessment and Treatment: Once risks are identified, organizations need to evaluate their severity and determine appropriate measures to mitigate those risks.
  • Continuous Monitoring and Improvement: Risk management is not a one-time effort; it requires continuous evaluation and adaptation of strategies to keep pace with evolving cybersecurity threats.

Operational Impacts and Compliance Challenges

Implementing effective risk management strategies brings a range of operational impacts, including:

  • Resource Allocation: Organizations must allocate sufficient resources—financial, human, and technological—to develop and maintain effective cybersecurity measures.
  • Cultural Shift: Shifting organizational culture to prioritize cybersecurity is vital. Employee training and awareness programs should become integral components of daily operations.
  • Integration of Technology: Organizations need to invest in comprehensive security technologies capable of supporting the desired risk management objectives.

Despite the clear directives established by NIS 2, many organizations encounter common compliance challenges, such as:

  • Identifying Applicability: Determining whether an organization falls under the essential or important entities category may lead to misinterpretations and oversight in compliance.
  • Resource Constraints: Smaller entities often lack the resources necessary to implement robust cybersecurity measures, raising concerns about their vulnerability to cyber incidents.

Practical Compliance Steps for NIS 2

To align with the NIS 2 Directive, organizations must undertake a series of actionable steps to ensure compliance and foster a resilient cybersecurity framework.

Required Policies and Procedures

  1. Cybersecurity Policy Development: Organizations should draft comprehensive cybersecurity policies outlining risk management objectives and procedures.
  2. Incident Response Plan: Develop a structured procedure for responding to cybersecurity incidents, including identification, containment, eradication, and recovery phases.
  3. Awareness and Training Programs: Regular employee training sessions can aid in cultivating a security-focused workforce and ensuring adherence to policies.

Documentation and Evidence

During audits or inspections, organizations are expected to provide documentation demonstrating compliance with NIS 2 requirements, including:

  • Incident Reports: Detailed logs of past incidents, how they were handled, and the lessons learned.
  • Risk Management Documentation: Reports evidencing risk assessments and the methodologies used to mitigate identified risks.
  • Training Records: Evidence of employee training programs and their effectiveness in mitigating cybersecurity risks.

Demonstrating Ongoing Compliance

To ensure ongoing adherence to NIS 2, organizations should consider the following best practices:

  • Regular Reviews and Updates: Conduct periodic reviews of cybersecurity policies and risk assessments to adapt to emerging threats.
  • Third-Party Assessments: Engage external auditors to evaluate compliance levels, ensuring objectivity and transparency in risk management practices.
  • Cross-border Collaborations: Foster partnerships with other organizations within the EU to share insights and best practices related to cybersecurity.

Conclusion

The EU NIS 2 Directive represents a pivotal shift toward a more robust and coordinated approach to cybersecurity across Europe. Organizations must prioritize compliance by establishing strong cybersecurity risk management frameworks that encompass thorough assessments, incident handling procedures, and ongoing training programs.

Recognizing the importance of structured and continuous compliance with the NIS 2 Directive is critical in navigating the increasing complexity of the cyber threat landscape. By taking proactive measures and fostering a culture of cybersecurity resilience, organizations can not only meet regulatory expectations but also protect their operations from ever-evolving cyber risks.

Posted on — Leave a comment

DORA – Ensuring Regulatory Compliance in Financial Services

Introduction

In an increasingly digital world, operational resilience has become a vital attribute for financial entities. The European Union’s Digital Operational Resilience Act (DORA) addresses this critical need by establishing a comprehensive regulatory framework aimed at bolstering the ICT resilience of the financial sector. Adopted as part of the broader Digital Finance Package, DORA strives to ensure that financial organizations can withstand and recover from disruptions caused by operational failures, cyber incidents, or any other form of information and communication technology (ICT) risk.

DORA’s objectives are to harmonize rules across the EU, enhancing the resilience of the financial system while establishing robust risk management frameworks for ICT. It encompasses a wide range of financial institutions, including banks, insurance companies, and investment firms, thereby promoting a cohesive approach to operational resilience across the member states.

Operational resilience and effective ICT risk management are more critical than ever. As financial services increasingly rely on digital technologies, the potential for systemic risks and cyber threats escalates, necessitating rigorous compliance standards to safeguard institutions and their clients.

The ICT Risk Management Framework: A Critical Component of DORA

Among the various operational aspects of DORA, the ICT risk management framework stands out as an essential focus area. This framework promotes a holistic approach to identifying, managing, and mitigating ICT-related risks. DORA mandates financial entities to create robust governance structures that specifically address ICT risk. This encompasses conducting thorough assessments, implementing effective control measures, and continuously monitoring risk exposures.

Operational Impacts and Compliance Challenges

Implementing an effective ICT risk management framework under DORA poses several operational challenges. Not only must institutions adapt their existing structures to comply with regulatory expectations, but they also need to integrate this framework into their overall risk management strategy. Common areas of difficulty include:

  1. Integration with existing risk management: Many financial entities may struggle to align ICT risk frameworks with enterprise risk management, causing inefficiencies or gaps in risk coverage.

  2. Data management and reporting: The increased demand for diverse data types raises concerns over data quality, accuracy, and completeness in reporting to regulatory agencies.

  3. Resource allocation: Developing a comprehensive risk management framework necessitates significant investment in resources and expertise, which can strain existing operational capacities.

Regulatory Expectations and Implementation Gaps

Regulatory expectations under DORA extend beyond mere compliance; they emphasize a proactive and dynamic approach to ICT risk management. Common implementation gaps include inconsistent risk assessment processes, insufficient documentation and evidence for audits, and delayed incident response mechanisms. Regulators expect financial entities to not only identify risks but also articulate plans for risk remediation and recovery that are regularly tested for effectiveness.

Practical Compliance Steps for Financial Entities

To align with DORA and establish a robust ICT risk management framework, financial entities must undertake a series of concrete steps:

Key Policies and Procedures

  1. Develop a Risk Management Policy: Establish a comprehensive ICT risk management policy that aligns with DORA and outlines roles, responsibilities, and procedures for assessing and mitigating risks.

  2. Conduct Risk Assessments: Regularly perform risk assessments to identify potential vulnerabilities and their impact on operational resilience. This should include both qualitative and quantitative measures.

  3. Implement Incident Response Plans: Create and maintain detailed incident response plans that define roles, processes, and communication strategies for addressing various ICT incidents.

Required Documentation

Financial institutions must maintain thorough documentation to evidence compliance during audits or inspections. This includes:

  • Records of risk assessments and mitigation strategies.
  • Incident reports and responses.
  • Testing documentation for risk management controls.
  • Training records for staff involved in risk management processes.

Best Practices for Ongoing Compliance

  1. Establish a Continuous Review Process: Regularly review and update risk management practices to ensure they remain effective and in line with regulatory expectations.

  2. Invest in Training: Conduct regular training for employees on ICT risk management and incident response procedures to enhance institutional awareness and preparedness.

  3. Engage Stakeholders: Foster a culture of resilience by involving all levels of management and cross-functional teams in resilience planning and testing initiatives.

  4. Leverage Technology: Use advanced technologies to automate risk assessments and monitoring, enhancing data accuracy and efficiency in reporting.

Conclusion

Navigating the EU Digital Operational Resilience Act (DORA) imposes significant responsibilities on financial entities. The ICT risk management framework is a cornerstone of this regulation, requiring institutions to adopt proactive measures, ensure compliance, and promote operational resilience in the face of evolving threats.

In summary, organizations must focus on developing comprehensive policies, conducting consistent risk assessments, and adhering to regulatory expectations to foster a culture of resilience. A structured and continuous approach to operational resilience will not only satisfy compliance mandates but will also ultimately protect institutions and their clients from the complex landscape of ICT risk. Engaging with these challenges will ensure that financial entities can thrive in a digitally-driven environment, ready to face the demands of tomorrow.