Posted on — Leave a comment

Compliance Strategies for Consultants

Introduction

In an increasingly interconnected world, the imperative for robust cybersecurity measures has never been more pressing. The EU NIS 2 Directive, which came into effect in 2022, is a cornerstone of European cybersecurity policy designed to enhance the overall level of security in network and information systems across the EU. This directive builds upon the original NIS Directive, expanding its scope and reinforcing its demands on both essential and important entities.

Overview of the EU NIS 2 Directive

The NIS 2 Directive aims to bolster the resilience and incident response capabilities of organizations that operate critical infrastructures. By establishing a comprehensive framework for cybersecurity risk management, the directive seeks to reduce the likelihood of disruptive cyber incidents affecting essential services such as energy supply, transportation, healthcare, and digital services.

Objectives and Scope of the Regulation

The primary objectives of the NIS 2 Directive include enhancing the cybersecurity posture of organizations, facilitating improved cooperation between EU member states, and fostering a culture of risk management. This directive applies to two categories of entities: essential entities, which provide critical services, and important entities, which, while perhaps less critical, still play vital roles in the economy and society.

Practical Implications for Organizations Subject to NIS 2

For organizations falling under the NIS 2 Directive, compliance is not optional—it is a necessity. Organizations must be prepared to implement comprehensive cybersecurity measures, respond effectively to incidents, and report breaches in a timely manner. Failure to comply could result in significant penalties, including fines and reputational damage.

Cybersecurity Risk Management Obligations

One of the most critical aspects of the NIS 2 Directive is its emphasis on cybersecurity risk management obligations. Organizations are now required to establish and maintain a comprehensive risk management framework that addresses their unique threat landscape. This requirement encompasses a range of activities aimed at identifying, assessing, and mitigating risks to their network and information systems.

Operational Impacts and Compliance Challenges

Organizations must recognize that the implementation of effective cybersecurity measures can have substantial operational implications. Companies may need to allocate resources for new technologies, hiring skilled cybersecurity professionals, and developing training programs for current staff. The challenge is not only to integrate these mechanisms into existing operational processes but also to ensure that they remain flexible and responsive to the evolving threat landscape.

Organizations may face common gaps when undertaking the necessary adjustments. Many find themselves lacking in adequate documentation of policies and procedures, insufficient staff training, or a lack of alignment between their cybersecurity posture and organizational risk appetite. As the NIS 2 Directive emphasizes continuous monitoring and improvement, businesses must proactively seek to address these issues.

Practical Compliance Section

Concrete Steps Organizations Must Take

  1. Risk Assessment: Conduct a thorough risk assessment to identify potential threats to network and information systems. This includes evaluating the impact and likelihood of various attack vectors.

  2. Develop Policies and Procedures: Establish cybersecurity policies that outline risk management practices, incident response protocols, and recovery strategies that align with NIS 2 obligations.

  3. Training and Awareness: Implement a staff training program to ensure that all employees understand their roles in maintaining cybersecurity hygiene and the importance of prompt incident reporting.

  4. Incident Management Framework: Create a structured incident management framework to enable rapid response to security breaches, including defining roles, responsibilities, and communication channels.

  5. Regular Audits: Schedule and conduct regular internal and external audits to assess compliance with NIS 2 requirements and identify areas for improvement.

Required Policies, Procedures, and Evidence

Organizations must document their policies and procedures for managing cybersecurity risks comprehensively. This includes:

  • Detailed incident response plans,
  • Evidence of risk assessments,
  • Records of employee training sessions,
  • Logs of security incidents, and
  • Documentation of audits and their findings.

Best Practices to Demonstrate Ongoing Compliance

To ensure ongoing compliance with NIS 2, organizations should adopt best practices such as:

  • Establishing a dedicated cybersecurity team,
  • Engaging with industry peers to share insights and improve resilience collectively,
  • Utilizing automated security tools to enhance monitoring and reporting capabilities,
  • Keeping abreast of technological advancements and emerging threats.

Conclusion

As we navigate the complex landscape of cybersecurity regulation in Europe, the EU NIS 2 Directive offers a structured framework to strengthen organizational resilience against cyber threats. The directive’s emphasis on risk management, incident response, and collaboration calls for proactive and sustained compliance efforts.

By adhering to the guidance set forth in NIS 2, organizations can not only fortify their defenses against cyber incidents but also cultivate a culture of security that benefits the entirety of the European digital economy. As the threat environment continues to evolve, a structured and continuous compliance approach will be crucial for any organization aiming to thrive in this complex regulatory ecosystem.
Posted on — Leave a comment

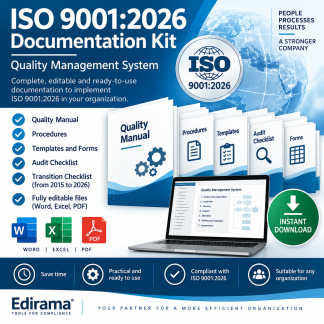
Navigating Key Changes in ISO 9001:2026 for Quality Management Systems

As organizations continue to adapt to changing market conditions and consumer demands, the importance of a robust Quality Management System (QMS) cannot be overstated. The forthcoming ISO 9001:2026 standard is designed to enhance the effectiveness of QMS, facilitating better alignment with modern business practices and technological advances. Understanding these changes is crucial for organizations already certified under ISO 9001:2015, as they navigate the transition towards this new standard.

What Changes with ISO 9001:2026

ISO 9001:2026 aims to refine several critical areas within the existing framework established by ISO 9001:2015. While the final details are yet to be formalized, organizations should prepare for significant modifications that may impact their QMS.

Key Focus Areas Expected in ISO 9001:2026

  • Integration of Digital Technologies: As digital transformation accelerates, ISO 9001:2026 is anticipated to incorporate requirements that encourage organizations to leverage technology to improve quality controls and drive operational efficiencies.

  • Risk-Based Thinking Evolution: The focus on risk management is likely to expand, emphasizing proactive risk identification and mitigation strategies, going beyond compliance to enhance overall organizational resilience.

  • Stakeholder Engagement: Greater emphasis on engaging not just customers, but other stakeholders in quality and operational decisions will be central to the new standard.

  • Sustainability and Social Responsibility: With increasing focus on environmental and social governance, expect a stronger emphasis on sustainable practices within the context of quality management.

Differences from ISO 9001:2015

Understanding how ISO 9001:2026 differs from ISO 9001:2015 is essential for organizations planning their transitions. Some expected changes include:

  • Language and Terminology Updates: Revised definitions and terminologies may provide better clarity in the application of quality management principles.

  • New Clauses or Requirements: While the structure remains similar, new clauses addressing modern challenges could emerge, necessitating updates to the QMS.

  • Change in Focus Areas: The reinvented emphasis on stakeholder engagement and sustainability may result in more detailed requirements affecting operational procedures.

Impact on the Quality Management System

Transitioning to ISO 9001:2026 will not only demand updates to documentation but will also require a reevaluation of existing processes within the QMS. Key impacts include:

  • Document Structure Revision: Organizations may need to change how they structure and present their QMS documentation, aligning it with the new clauses and focus areas.

  • Process Alignment: Current operational processes should be assessed for alignment with new expectations, ensuring they meet the enhanced requirements for stakeholder engagement and risk management.

  • Increased Internal Communication: Greater emphasis on stakeholder involvement necessitates improved internal communication strategies to facilitate collaboration and input from various departments.

Documents and Procedures to Review

As ISO 9001:2026 is implemented, organizations should focus on the following documents and procedures for review and potential updates:

  • Quality Manual: This should reflect updates in scope or objectives as defined by the new standard.

  • Procedures and Work Instructions: Processes related to risk management, stakeholder engagement, and technology integration will need examination and potentially significant revisions.

  • Quality Objectives: These should be revisited to ensure they align with any new expectations set forth in the upcoming standard.

  • Internal Audit Protocols: Auditing processes may need adjustment to incorporate any new compliance checklists or focus areas introduced in ISO 9001:2026.

What Quality Managers Should Do

Quality Managers play a pivotal role in the transition to ISO 9001:2026. They need to:

  • Conduct a Gap Analysis: This is critical to identify areas where the current QMS fails to meet the expectations of ISO 9001:2026. It will help outline specific areas for improvement and establish an action plan.

  • Engage Stakeholders: Gathering input from various stakeholders early in the process will ensure that the QMS is inclusive and meets the needs of all affected parties.

  • Training and Development: Ensure that all employees involved in quality management processes are informed about the changes and trained on the new requirements.

  • Update Training Materials: Materials should reflect any changes arising from the transition, facilitating smoother training sessions for current and new employees.

How to Prepare for the Transition

Preparation for ISO 9001:2026 should be strategic and thorough. Here are steps organizations can take:

  • Start Early: Begin the transition process as soon as possible to allow ample time for necessary adjustments across the organization.

  • Communicate Plans: Internal communication is critical; inform all employees about upcoming changes and the importance of their roles in the transition.

  • Review Existing QMS: Assess the existing QMS documentation, processes, and practices against ISO 9001:2026 expectations to identify gaps.

  • Develop an Action Plan: Create a comprehensive action plan detailing steps, responsibilities, and timelines for adjustments and improvements.

  • Stay Informed: Keep abreast of any updates from ISO regarding final requirements as the standard progresses from proposal to publication.

How to Prepare for ISO 9001:2026

Successfully transitioning to ISO 9001:2026 requires diligence and proactive measures.

  • Conduct a Gap Analysis: This essential first step allows organizations to pinpoint discrepancies between their current QMS and the new requirements.

  • Review Quality Manual and Procedures: Evaluate and, if necessary, revise the Quality Manual, procedures, forms, and other documentation in light of the anticipated changes.

  • Internal Audits: Regular internal audits will help evaluate current practices against expected standards, uncovering areas that need adjustment.

By implementing a thorough review of existing documentation, processes, and personnel understanding, organizations can ensure they are well-prepared for the transition to ISO 9001:2026. Emphasizing a commitment to quality throughout this period will further solidify an organization’s reputation as a leader in quality management.

Posted on — Leave a comment

NIS 2 – Strengthening Cybersecurity Regulations for Organizations

Introduction

The EU NIS 2 Directive represents a significant advancement in cybersecurity regulation across Europe. Established to enhance the security of network and information systems, the directive targets multiple sectors, including essential and important services. By expanding the scope of regulation to cover not only traditional critical infrastructures such as energy and transport but also digital services and public administrations, NIS 2 aims to fortify the EU’s overall cybersecurity posture.

Objectives and Scope of the Regulation

The primary objectives of NIS 2 are to increase the resilience of the EU’s cybersecurity landscape and to collectively improve the ability to prevent and respond to incidents. Key areas include:

  • Establishing a coherent cybersecurity framework across member states
  • Enhancing the capacities of national authorities
  • Mandating stringent cybersecurity risk management practices among businesses and organizations

The directive encompasses both “essential entities,” which are critical to the maintenance of vital societal functions, and “important entities” whose disruption could lead to significant economic or societal impact.

Practical Implications for Organizations Subject to NIS 2

Organizations designated under NIS 2 must now navigate a more comprehensive regulatory environment. Compliance isn’t merely about checking boxes; it involves an ongoing commitment to enhancing cybersecurity preparedness and resilience.

Focus Topic: Cybersecurity Risk Management Obligations

Operational Impacts and Compliance Challenges

Cybersecurity risk management obligations under NIS 2 are among the most critical aspects of compliance. Organizations must establish and maintain a robust risk management framework that is integrated into their overall governance practices. This includes conducting regular risk assessments, implementing appropriate technical and organizational measures, and continuously reviewing these strategies in response to emerging threats.

The operational impacts of these obligations can be profound. Organizations are expected to:

  • Allocate resources to regularly assess risks
  • Develop a holistic approach to cybersecurity that includes personnel, processes, and technology
  • Engage in periodic audits to identify compliance gaps

However, many organizations struggle with these requirements due to a lack of understanding or resources. This sows confusion around risk reporting and the adequacy of existing security measures.

Common Gaps and Regulatory Expectations

Non-compliance can result in significant legal and financial repercussions. Common gaps that organizations encounter include:

  • Insufficient documentation of risk assessments
  • Failure to enact recommended technical controls
  • Lack of awareness or training among staff regarding cybersecurity policies

To align with regulatory expectations, organizations must ensure that risk management efforts are not only implemented but continuously refined and adapted to address new threats and vulnerabilities.

Practical Compliance Section

Concrete Steps Organizations Must Take

To ensure compliance with NIS 2 directives, organizations can consider the following actionable steps:

  1. Establish a Compliance Framework: Define a clear risk management framework that aligns with NIS 2 requirements.
  2. Conduct Thorough Risk Assessments: Regularly evaluate the security landscape and vulnerabilities specific to the organization.
  3. Implement Technical Controls: Invest in appropriate cybersecurity technologies—firewalls, intrusion detection systems, and encryption measures.
  4. Develop Incident Response Plans: Prepare structured response plans for potential security breaches and ensure all employees are trained in their roles.
  5. Create Documentation Protocols: Maintain thorough records of risk assessments, incident reports, and compliance measures taken.

Required Policies, Procedures, and Evidence

Documentation plays a critical role not only in compliance but in demonstrating compliance during audits. Organizations should have:

  • Documented risk management policies
  • Incident response plans and incident logs
  • Training records for staff on cybersecurity protocols
  • Previous audit results and remediation actions taken

Best Practices to Demonstrate Ongoing Compliance

Beyond documentation, organizations should:

  • Regularly review and update cybersecurity policies
  • Foster a culture of security awareness among all employees
  • Engage with external advisors or consultants for third-party assessments

Conclusion

The EU NIS 2 Directive significantly reshapes the cybersecurity landscape for organizations across multiple sectors. With clearly defined obligations around cybersecurity risk management, organizations must now adopt a structured approach to compliance.

In summary, organizations must not only adhere to existing regulatory requirements but also cultivate a culture of cybersecurity that anticipates and mitigates risks effectively. A commitment to continuous improvement in cybersecurity practices will ensure that organizations not only comply with NIS 2 but also enhance their resilience against a constantly evolving threat landscape.

As the digital world progresses, so should the strategies to protect it. Addressing the requirements of NIS 2 is not just a regulatory obligation but a fundamental business imperative.

Posted on — Leave a comment

NIS 2 – Essential Compliance Strategies for Cybersecurity Leaders

Introduction

The European Union’s NIS 2 Directive, an essential piece of legislation aimed at enhancing cybersecurity resilience across the EU, came into effect to address the evolving threat landscape faced by essential and important entities. This directive builds upon its predecessor, the original NIS Directive, and provides a more comprehensive framework that targets a wider scope of organizations and sectors. Its main objectives are to improve the overall cybersecurity posture of member states, enhance cooperation in cybersecurity, and ensure that entities adopt robust security measures to protect their networks and information systems.

The NIS 2 Directive applies to a broad range of sectors, including energy, transport, health, and digital services, among others. It mandates strict cybersecurity requirements, incident notification protocols, and supervisory measures. The implications for organizations subject to this regulation are profound, requiring immediate attention from cybersecurity professionals, compliance officers, and executive management to ensure adherence.

Cybersecurity Risk Management Obligations

A critical component of the NIS 2 Directive is the emphasis on cybersecurity risk management obligations. Organizations classified as essential or important entities must adopt a risk-based approach to cybersecurity, aligning their practices with industry standards and best practices. This section details operational impacts, compliance challenges, and the expectations set by the NIS 2 framework.

Operational Impacts and Compliance Challenges

The directive requires organizations to implement a comprehensively defined risk management framework. This includes not only the identification and assessment of cybersecurity risks but also the establishment of relevant risk treatment measures. The operational impacts of these obligations require entities to integrate risk management into their day-to-day operations, which may necessitate a cultural shift within organizations that have not previously prioritized cybersecurity.

Compliance challenges may arise from several frontiers:

  • Resource Allocation: Proper risk management requires investment in technology, personnel training, and ongoing assessments. Smaller enterprises may struggle with limited budgets and resources.
  • Complex Internal Processes: Organizations with existing cybersecurity frameworks may find it challenging to integrate NIS 2 requirements into pre-existing processes.
  • Inconsistent Reporting Structures: Clear governance structures must be established, which can be a challenge for entities lacking defined roles in cybersecurity responsibilities.

Common Gaps and Regulatory Expectations

Common gaps may include inadequate risk assessments, insufficient mitigation strategies for identified risks, and lack of documentation regarding these processes. The NIS 2 Directive expects organizations to fill these gaps by establishing a documented risk management plan that outlines how cybersecurity risks will be monitored, reported, and addressed.

Additionally, the directive highlights the importance of adopting a culture of continuous improvement regarding cybersecurity practices, which necessitates both a proactive and reactive strategy that evolves with emerging threats.

Practical Compliance Section

Achieving compliance with the NIS 2 Directive involves multiple concrete steps. Organizations must establish and maintain clear policies and procedures, which can serve as the bedrock for compliance efforts.

Required Policies, Procedures, and Evidence

  1. Risk Management Policy: Organizations should develop and document comprehensive risk management policies detailing their approach to identifying, assessing, and mitigating cybersecurity risks.

  2. Incident Response Plan: Mandatory under the directive, these plans should define processes for detecting, responding to, and recovering from cybersecurity incidents, including timelines and roles.

  3. Security Training: Regular training programs for employees at all levels can help foster a culture of cybersecurity awareness and responsibility.

  4. Systematic Documentation: Evidence of compliance, such as risk assessments, incident reports, and mitigation measures, must be meticulously documented to withstand scrutiny during audits or inspections.

Best Practices for Ongoing Compliance

  • Engage in Regular Audits: Conduct thorough internal and external audits to ensure existing cybersecurity measures align with NIS 2 requirements.
  • Continuously Update Risk Assessments: Given the dynamic nature of cyber threats, risk assessments should not be a one-time effort but rather an ongoing process.
  • Collaborate and Share Information: Cooperation within sectors and with national cybersecurity authorities can enhance situational awareness and improve overall cyber resilience.

Conclusion

In summary, the EU’s NIS 2 Directive represents a significant advancement in strengthening cybersecurity measures and governance across essential and important entities. The key points outlined—emphasizing risk management obligations, operational impacts, and practical compliance measures—underscore the importance of a structured and continuous approach to compliance. To thrive in an increasingly complex regulatory landscape, organizations must embrace cybersecurity as a fundamental component of their operations, safeguarding not only their own assets but also the critical infrastructures they support. By adopting a proactive stance on compliance with the NIS 2 Directive, organizations can ensure resilience against cyber threats, building a stronger and more secure digital ecosystem for all.

Posted on — Leave a comment

ISO 9001:2026 Updates on Risk Management Requirements for Quality Systems

Navigating the Transition to ISO 9001:2026: A Practical Guide for Organizations

As the landscape of quality management continues to evolve, the upcoming ISO 9001:2026 standard will introduce significant shifts that certified organizations must navigate effectively. Understanding these changes is crucial for maintaining compliance and ensuring continuous improvement in the quality management systems (QMS). This article aims to provide comprehensive insights into ISO 9001:2026, detailing its implications for organizations currently adhering to ISO 9001:2015.

What Changes with ISO 9001:2026

ISO 9001:2026 is expected to enhance several key aspects of the quality management framework. The revisions aim to address the evolving market needs, technological advancements, and an increased focus on sustainability and stakeholder engagement. While the specific finalized requirements will be detailed in the official release, organizations can anticipate a more integrated approach to managing quality that may include:

  • Emphasis on Digital Transformation: Organizations may be encouraged to leverage technologies that support better process management and data analysis.
  • Sustainability Considerations: Greater attention to sustainable practices and environmental considerations will likely be incorporated.
  • Stakeholder Inclusion: A broader view of stakeholder needs, including supply chain partners, workforce, and customers, may be outlined.

These aspects aim to enhance the relevance and effectiveness of the standard in a changing business environment.

Differences from ISO 9001:2015

Significant updates expected in ISO 9001:2026 compared to the 2015 version include:

  • Risk Management Evolution: The framework around risk-based thinking may be refined to better align with strategic objectives.
  • Integration with Other Standards: ISO 9001:2026 may propose improvements in the compatibility of QMS with other management systems, potentially simplifying the integration process for organizations with multiple certifications.
  • Reporting and Transparency Enhancements: There could be new requirements for transparency in reporting quality performance, aligning organizational practices with stakeholder expectations.

It’s important to note that these expected changes are based on draft proposals and subject to final confirmation upon release.

Impact on the Quality Management System

Transitioning to ISO 9001:2026 will necessitate a thorough review of an organization’s current Quality Management System. Key implications include:

  • Systematic Updates: QMS protocols may need revision to align with the new focus areas, especially in risk management and stakeholder engagement strategies.
  • Training and Awareness: Training programs should be adapted to include the new standard requirements, ensuring all staff are equipped with the necessary knowledge and skills.
  • Auditing Processes: Audit procedures may need redefinition to encompass the revised criteria and expectations, ensuring compliance and continuous improvement.

Documents and Procedures to Review

To facilitate compliance with ISO 9001:2026, organizations should prioritize several key documents and procedures for review:

  • Quality Manual: Ensure it reflects updates in organizational objectives and the inclusion of sustainability and stakeholder engagement strategies.
  • Risk Management Documentation: Reassess current risk management strategies to incorporate any new requirements around risk assessment and opportunities.
  • Internal Audit Procedures: Revise internal audit policies and checklists to align with new standards for performance reporting and transparency.
  • Training Materials: Develop training resources that reflect the specifics of ISO 9001:2026 and prepare staff for the upcoming changes.

What Quality Managers Should Do

Quality managers play a pivotal role in ensuring a smooth transition to ISO 9001:2026. Key actions include:

  • Gap Analysis: Conduct a Gap Analysis against the new standard to identify areas needing improvement or redefinition.
  • Stakeholder Engagement: Initiate discussions with stakeholders to understand their needs and expectations, ensuring that the organization’s QMS remains relevant.
  • Impact Assessment: Assess the impact of each proposed change on current processes, engaging relevant teams in the evaluation.
  • Document Updates: Begin the process of updating documentation and procedures as new requirements become clear.

How to Prepare for the Transition

Preparing for the transition to ISO 9001:2026 involves a structured approach. Organizations should consider the following steps:

  1. Conduct a Gap Analysis: This analysis will identify discrepancies between the current ISO 9001:2015 practices and what will be required under ISO 9001:2026.
  2. Review and Update Key Documentation: Focus on revising the Quality Manual, process documentation, and any supporting records in line with the anticipated changes.
  3. Engage Employees: Involve employees in the preparation process through training sessions, workshops, and information sharing to foster a culture of understanding and compliance.
  4. Develop an Implementation Plan: Formulate a clear plan that outlines timelines, responsibilities, and milestones leading up to the transition.

How to Prepare for ISO 9001:2026

In conclusion, the transition from ISO 9001:2015 to ISO 9001:2026 will require organizations to stay proactive and prepared. A thorough Gap Analysis will be essential to identify and address discrepancies between current practices and upcoming requirements. Key documents such as the Quality Manual, procedures, and forms must be diligently reviewed and updated to align with the new standard.

Quality Managers should lead the charge in managing this transition, ensuring that internal audits and the overall Quality Management System documentation remain compliant and reflect best practices. By staying informed and engaged with the updates, organizations will not only better manage the transition but also enhance their quality management practices going forward.

Posted on — Leave a comment

DORA – Ensuring Financial Compliance in ICT Risk Management

Overview of the EU Digital Operational Resilience Act (DORA)

The EU Digital Operational Resilience Act (DORA), which came into effect in January 2023, marks a pivotal step in enhancing the operational resilience of financial entities within the European Union. It aims to ensure that financial institutions can withstand, respond to, and recover from all types of ICT-related disruptions and threats. As digital transformation accelerates, operational resilience becomes increasingly crucial, with regulation now focusing not only on preventing incidents but also on the capacity to manage and recover from them effectively.

Objectives and Regulatory Scope

The primary objectives of DORA are to establish a harmonized framework for ICT risk management, enhance the stability of the financial system, and protect consumers and investors from the ramifications of ICT failures. DORA requires financial entities to implement robust governance and risk management frameworks that account for ICT risks while also addressing the complex web of third-party dependencies.

Why Operational Resilience and ICT Risk Management Are Critical

The growing reliance on technology in the financial sector has heightened the risks associated with ICT disruptions, making operational resilience essential to safeguard financial stability. Effective ICT risk management not only protects firms from financial losses but also fortifies customer trust and regulatory compliance.

ICT Risk Management Framework

The Importance of a Robust ICT Risk Management Framework

One of the cornerstones of DORA is the establishment of a comprehensive ICT risk management framework. Financial entities must identify, assess, and prioritize ICT risks using a risk-based approach. This framework must encompass all aspects of ICT, including infrastructure, applications, and processes, to effectively address the multifaceted nature of these risks.

Operational Impacts and Compliance Challenges

Financial institutions may face various operational impacts when developing an ICT risk management framework. These include the need for significant investment in technology and personnel, the complexity of integrating new systems with legacy infrastructures, and the challenge of cultivating a culture of risk awareness throughout the organization. Compliance challenges may arise from a lack of clear guidance on specific risk metrics or assessment methodologies, resulting in inconsistent implementation across different institutions.

Regulatory Expectations and Common Implementation Gaps

Regulators expect financial entities to adopt a holistic view of ICT risks, integrating them into their overall risk management frameworks. Common implementation gaps may involve incomplete assessments of third-party risks, inadequate incident response plans, or insufficient training of staff concerning ICT risk management principles. Additionally, financial entities often struggle to maintain appropriate documentation that satisfies regulatory scrutiny.

Practical Compliance Steps

Concrete Steps Financial Entities Must Take

The implementation of DORA requires a series of concrete steps by financial entities to ensure compliance. These include:

  • Conducting a Comprehensive Risk Assessment: Identify and evaluate potential ICT-related risks, focusing on both internal and external threats.

  • Developing a Robust ICT Risk Management Policy: Formulate a policy that delineates the governance structure, roles, and responsibilities related to ICT risk management.

  • Implementing Incident Reporting and Response Protocols: Establish clear reporting lines for ICT incidents and develop coherent response protocols to manage incidents swiftly and effectively.

Required Policies, Procedures, and Control Frameworks

Financial entities must create and maintain several key documents, including:

  • ICT Risk Management Framework: This document should outline the entity’s approach to identifying, assessing, and mitigating ICT risks.

  • Third-Party Risk Management Policy: Detail the criteria for assessing third-party service providers and stipulate ongoing monitoring processes.

  • Incident Management Procedures: Clearly defined steps for responding to and recovering from ICT incidents are essential for resilience.

Evidence and Documentation Expected During Audits or Inspections

To demonstrate compliance during audits, institutions should maintain comprehensive records, such as:

  • Risk assessment reports
  • Policy documents outlining ICT risk management practices
  • Records of incidents and their resolutions
  • Training logs for employee awareness programs related to ICT risks

Best Practices to Demonstrate Ongoing DORA Compliance

Financial institutions should adopt best practices such as:

  • Continuous Monitoring: Regularly review and update risk assessments and mitigation strategies to remain aligned with evolving threats and regulatory expectations.

  • Employee Training: Foster a risk-aware culture by providing ongoing training sessions for all employees regarding ICT risks and incident response.

  • Engaging Third-Party Auditors: Consider engaging external auditors for independent assessments of compliance with DORA requirements, facilitating the identification of potential weaknesses.

Conclusion

In summary, the EU Digital Operational Resilience Act (DORA) represents a crucial advance in the regulatory landscape governing operational resilience for financial entities. By establishing clear expectations regarding ICT risk management frameworks, incident reporting, and third-party dependencies, DORA compels organizations to strengthen their resilience capabilities significantly. It is imperative that financial institutions adopt a structured and continuous approach to operational resilience, ensuring that they can navigate the complexities of today’s digital environment while remaining compliant with rigorous regulatory standards.

Posted on — Leave a comment

NIS 2 – Navigating Compliance Challenges in Cybersecurity Standards

Introduction

The EU NIS 2 Directive is a significant regulatory development aimed at enhancing the cybersecurity resilience of the European Union’s critical infrastructure and essential services. Building upon the original NIS Directive, the NIS 2 Directive addresses the fast-evolving cyber threat landscape and reinforces the obligations for both essential and important entities operating within the EU member states.

The primary objective of the NIS 2 Directive is to elevate overall cybersecurity standards across the EU, ensuring a unified approach to risk management and incident response. The scope of this directive includes a broad range of sectors, such as energy, transport, health, and digital infrastructure, mandating stringent cybersecurity measures.

For organizations classified as essential and important entities, compliance with the NIS 2 Directive imposes significant operational requirements and necessitates a thorough understanding of the regulatory landscape.

Understanding Cybersecurity Risk Management Obligations

One critical aspect of the NIS 2 Directive is the emphasis on cybersecurity risk management obligations. Organizations are required to assess potential risks to their systems and services continually. This includes both internal processes and external threats, reflecting the need for a comprehensive risk management framework.

Operational Impacts and Compliance Challenges

The operational impact of these obligations can be profound. Organizations must not only adopt a cybersecurity risk management framework but also ensure continuous monitoring and updating of their risk assessments in response to new threats. This requirement poses several challenges:

  1. Resource Allocation: Many organizations may struggle to allocate sufficient resources—both financial and human—to develop and maintain effective risk management programs.

  2. Skill Gaps: The demand for cybersecurity expertise is high, and many organizations face difficulties attracting and retaining skilled professionals capable of addressing complex security challenges.

  3. Cultural Integration: Ensuring that cybersecurity risk management is part of the organizational culture can be challenging, especially if there is resistance to change among employees and management.

Common Gaps and Regulatory Expectations

Regulatory expectations under the NIS 2 Directive highlight common gaps that organizations must address. For example, many organizations underestimate the importance of documenting risk assessments and associated mitigations. They may also fall short in integrating cybersecurity into their overall business strategy, which can lead to compliance issues.

Practical Compliance Section

To align with the NIS 2 Directive, organizations should take several concrete steps toward compliance:

Required Policies and Procedures

  1. Develop a Risk Management Framework: Establish a standardized risk management policy that includes risk identification, assessment, response, and monitoring.

  2. Incident Response Plan: Create a robust incident response plan that outlines procedures for identifying, managing, and reporting incidents.

Documentation Expectations

During audits or inspections, organizations must provide comprehensive documentation, including:

  • Risk assessments and justifications for chosen risk management measures.
  • Incident reports detailing how incidents were managed and lessons learned.
  • Policies addressing employee training and awareness regarding cybersecurity protocols.

Best Practices for Ongoing Compliance

  1. Regular Training: Conduct regular training sessions for employees to ensure they are aware of their role in maintaining compliance and protecting organizational assets.

  2. Engage Stakeholders: Involve different departments in discussions about cybersecurity to foster a collaborative approach and share ownership of cybersecurity initiatives.

  3. Continuous Monitoring: Implement a continuous monitoring strategy for both IT and OT environments, ensuring real-time detection of vulnerabilities and incidents.

  4. Third-Party Risk Management: Establish a third-party risk management program to assess and mitigate risks arising from vendors and other external entities.

Conclusion

The EU NIS 2 Directive imposes significant obligations on organizations, mandating a structured and proactive approach to cybersecurity risk management. By understanding the implications of these regulations and investing in the necessary resources and expertise, organizations can enhance their cybersecurity resilience and ensure compliance.

In summary, compliance with the NIS 2 Directive requires a holistic understanding of cybersecurity risk, effective incident management, and ongoing organizational commitment. As the cyber threat landscape continues to evolve, a structured and continuous compliance approach will be vital in safeguarding essential services and critical infrastructure across the EU.

Posted on — Leave a comment

DORA – Enhancing ICT Compliance for Financial Entities Resilience

Introduction

The EU Digital Operational Resilience Act (DORA) represents a significant regulatory initiative aimed at enhancing the operational resilience of financial entities across the European Union. Enacted as part of the EU’s broader digital finance strategy, DORA sets forth a framework for managing Information and Communication Technology (ICT) risks, thereby ensuring that financial organizations can withstand, respond to, and recover from all types of operational disruptions.

Objectives and Regulatory Scope

DORA seeks to establish a comprehensive approach to the regulation of operational resilience, specifically targeting the financial sector’s reliance on digital technologies. The Act outlines requirements that encompass governance, risk management, incident reporting, and testing of operational resilience practices, thereby emphasizing the significance of ICT risk management at all levels of financial organizations. DORA applies to a wide array of financial entities, including banks, investment firms, and insurance companies, thereby creating a standardized framework to address the increasing complexity and interconnectedness of ICT systems within the industry.

Why Operational Resilience and ICT Risk Management Are Critical

With the rise of digital services and the integration of technology in financial operations, the potential impact of ICT disruptions has grown exponentially. Operational resilience is not merely about preventing incidents; it’s also about preparing for, responding to, and recovering from them effectively. DORA enforces a cultural shift towards proactive risk management, which is crucial in maintaining trust and stability in financial markets.

ICT Risk Management Framework: Key Component of DORA

Understanding the ICT Risk Management Framework under DORA

A crucial aspect of DORA is the ICT risk management framework, which provides guidelines for establishing robust governance structures and risk management practices. This framework requires financial entities to assess and mitigate ICT risks that could disrupt operations. It mandates that organizations implement comprehensive strategies, ensuring alignment with overall business objectives and regulatory requirements.

Operational Impacts and Compliance Challenges

Implementing an effective ICT risk management framework under DORA poses several operational impacts and compliance challenges:

  • Resource Allocation: Entities may need to invest significant resources to establish or enhance their Risk Management Functions, including hiring skilled personnel, investing in advanced technologies, or updating existing infrastructures.

  • Cultural Shift: Organizations must cultivate a risk-aware culture where employees at all levels understand the importance of operational resilience and actively participate in risk management practices.

  • Integration with Business Processes: The challenge lies in aligning ICT risk management practices with existing business processes and ensuring that risks are managed consistently across the organization.

Regulatory Expectations and Common Implementation Gaps

The expectations set forth by DORA include clear delineation of roles and responsibilities in ICT risk management, comprehensive risk assessments, and continuous monitoring of risk controls. However, common gaps in implementation often arise from:

  • Insufficient Risk Assessment: Many entities struggle with conducting regular, thorough risk assessments which form the foundation of a strong risk management framework.

  • Inadequate Documentation: Maintaining proper documentation is vital for compliance, yet many organizations fall short in establishing a comprehensive record of their risk management activities.

  • Poor Reporting Mechanisms: Effective reporting processes are essential for timely notifications of incidents but are frequently lacking in operational plans.

Practical Compliance Section: Steps for Alignment with DORA

Concrete Steps Financial Entities Must Take

To align with DORA’s ICT risk management requirements, financial entities should consider the following steps:

  1. Develop a Comprehensive ICT Risk Management Policy: This policy should outline the organization’s approach to recognizing, measuring, and mitigating ICT risks.

  2. Conduct Regular Risk Assessments: Establish a schedule for periodic assessments to identify vulnerabilities and gaps in resilience.

  3. Implement a Risk Register: Maintain a risk register that details identified risks, potential impact, and corresponding mitigation strategies.

  4. Train Employees on Risk Awareness: Regular training sessions should be conducted to educate staff on ICT risks and their roles in managing them.

  5. Create Incident Response Plans: Detailed plans should outline procedures for responding to different types of ICT incidents, ensuring rapid resolution.

Required Policies, Procedures, and Control Frameworks

DORA compliance necessitates the development of formalized procedures and control frameworks that include:

  • Incident management frameworks that allow for seamless communication and reporting.
  • Change management policies to ensure that all changes to ICT systems are planned, tested, and documented.
  • Continuous monitoring controls that detect anomalies in ICT operations.

Evidence and Documentation Expected During Audits or Inspections

During audits or inspections, organizations must be able to provide:

  • Risk assessment reports demonstrating the assessment process and findings.
  • Incident logs that detail any ICT disruptions and how they were addressed.
  • Training records that show employees have been educated on the policies in place.

Best Practices to Demonstrate Ongoing DORA Compliance

To showcase ongoing compliance, entities should:

  • Regularly review and update their ICT risk management policies to reflect changes in the operational environment.
  • Foster a culture of accountability where employees understand and embrace their role in maintaining operational resilience.
  • Utilize metrics and KPIs to track the effectiveness of their ICT risk management framework continually.

Conclusion

In summary, the EU Digital Operational Resilience Act (DORA) sets forth a robust framework aimed at enhancing operational resilience within the financial sector. By focusing on ICT risk management, financial entities can align their operational practices with regulatory requirements while safeguarding their operations against potential disruptions. A proactive, structured, and continuous approach to managing ICT risks will not only fulfill regulatory obligations but will also bolster the overall integrity and trust within the financial ecosystem. Embracing these principles will position organizations not only for compliance but also for enduring success in an increasingly digitized regulatory landscape.

Posted on — Leave a comment

ISO 9001:2026 Updates: Key Impact on Quality Management Systems and Auditing

Transitioning to ISO 9001:2026: Preparing Your Organization for Change

As organizations globally strive for excellence in Quality Management Systems (QMS), the impending release of ISO 9001:2026 presents both challenges and opportunities. For those already certified under ISO 9001:2015, understanding the forthcoming changes is crucial to ensure a seamless transition and maintain compliance. This article will outline significant developments in ISO 9001:2026, their practical implications, and what actions organizations should take proactively.

What Changes with ISO 9001:2026

ISO 9001:2026 brings various enhancements aimed at fostering a more coherent and efficient approach to quality management. While specific details are still under discussion, some anticipated changes have been outlined in the drafts circulated during the development process. Key areas of focus include:

  1. Emphasis on Leadership and Commitment: Recognizing the importance of top management in embedding a culture of quality throughout the organization.

  2. Enhanced Risk Management: An expansion in the scope and application of risk-based thinking, moving beyond initial identification to continuous management and monitoring of risks.

  3. Alignment with Strategic Objectives: Affected organizations will need to ensure that their QMS aligns more closely with overall strategic objectives, facilitating better decision-making and long-term sustainability.

Differences from ISO 9001:2015

While many principles of ISO 9001:2015 remain intact, ISO 9001:2026 will likely introduce subtle shifts, including:

  • Stronger focus on stakeholder satisfaction: The new standard is expected to highlight the need for understanding and addressing the expectations of all stakeholders, rather than just customers.

  • Increased integration with other management systems: ISO 9001:2026 aims to facilitate easier integration with other ISO standards, such as ISO 14001 and ISO 45001, fostering a more holistic approach to organizational management.

  • Streamlined documentation requirements: Changes may simplify documentation processes, encouraging organizations to move towards a more agile and less bureaucratic QMS.

Impact on the Quality Management System

Transitioning to ISO 9001:2026 will have significant effects on an organization’s QMS. Here are some potential impacts:

  • Review of Existing Processes: Organizations may find that several current processes, particularly those relating to risk management and stakeholder engagement, require re-evaluation and redesign.

  • Training Needs: To lead an effective transition, training initiatives must be developed to ensure that all staff are aware of the new requirements and the importance of their roles in implementing the updated QMS.

  • Cultural Adaptation: A shift towards a more proactive quality culture may necessitate alterations in management approaches and employee engagement strategies.

Documents and Procedures to Review

In preparation for the transition to ISO 9001:2026, organizations should focus on updating several critical documents and procedures:

  • Quality Manual: Review and amend the Quality Manual to reflect new mandates, ensuring alignment with strategic objectives.

  • Risk Assessment Processes: Evaluate and enhance existing risk assessment and management processes, making sure they fulfill the expected depth in ISO 9001:2026.

  • Stakeholder Engagement Policies: Documentation related to stakeholder feedback mechanisms should be reassessed and adapted to reflect a broader engagement strategy.

  • Internal Audit Processes: Ensure that internal audits cover the new requirements of ISO 9001:2026, identifying any areas of non-compliance and potential improvement.

What Quality Managers Should Do

Quality Managers play a critical role in the transition process. Here’s what they should focus on:

  • Conduct a Gap Analysis: A thorough ISO 9001 Gap Analysis should be performed. This helps identify discrepancies between the current quality practices and the new requirements.

  • Engage Top Management: Initiate discussions with top management to secure support and commitment towards the necessary changes, reinforcing the importance of leadership in quality management.

  • Incorporate Stakeholder Perspectives: Gather input from diverse stakeholders to understand their expectations and structure strategies around their needs.

  • Develop an Action Plan: Create a detailed action plan based on the Gap Analysis findings to prioritize required changes and allocate resources effectively.

How to Prepare for the Transition

Preparing for the transition to ISO 9001:2026 involves strategic planning and proactive measures. Here are actionable steps organizations can take:

  • Training and Awareness: Organize training sessions on the new standard to enhance understanding among employees and equip them with the necessary skills to comply with updated requirements.

  • Collaborate with ISO Consultants: Engage with ISO consultants for expert guidance throughout the transition process, ensuring that best practices are followed meticulously.

  • Monitor Draft Standard Updates: Stay informed about the latest drafts and modifications leading up to the final publication of ISO 9001:2026 to adapt strategies in real-time.

  • Regular Review Meetings: Schedule review meetings with cross-functional teams to monitor progress and address any challenges arisen during the transition efforts.

How to Prepare for ISO 9001:2026

As the ISO 9001:2026 standard approaches its release, organizations must take decisive steps to prepare for its requirements. Conducting a Gap Analysis should be at the forefront of this preparation, allowing organizations to identify and rectify discrepancies well ahead of the transition deadline. Additionally, take the time to review the Quality Manual, assess existing procedures, and scrutinize forms and documentation to ensure they meet the latest demands.

In conclusion, transitioning to ISO 9001:2026 brings vital enhancements that can significantly improve your Quality Management System. Organizations that proactively adapt to these changes will not only achieve compliance but will also position themselves for sustained quality excellence in their operations.

Posted on — Leave a comment

DORA – Ensuring Compliance in Financial ICT Risk Management

Introduction

The EU Digital Operational Resilience Act (DORA) represents a significant regulatory framework aimed at bolstering the digital resilience of financial entities across the European Union. As digitalization accelerates, so too does the complexity of threats facing the financial sector, necessitating a comprehensive approach to operational resilience and ICT risk management. DORA’s primary objectives are to ensure that financial services can withstand, respond to, and recover from all types of ICT-related disruptions and cyber threats.

Objectives and Regulatory Scope

DORA applies to a broad spectrum of financial entities, including banks, investment firms, payment service providers, and insurance companies, among others. The regulation’s scope encompasses several critical areas, such as incident classification and reporting, digital operational resilience testing, and ICT third-party risk management. Understanding the nuances of DORA is vital not only for compliance officers and risk managers but also for executive management and audit functions, as operational resilience is pivotal in safeguarding both reputational and economic value.

Why Operational Resilience and ICT Risk Management Are Critical

Operational resilience within the financial sector is crucial in maintaining trust and stability in markets, particularly in times of crisis. Effective ICT risk management allows entities to manage the risk of cyber threats and operational disruptions—ensuring they can continue delivering essential services to customers and stakeholders.

ICT Risk Management Framework under DORA

Establishing an Effective ICT Risk Management Framework

At the core of DORA’s requirements lies a robust ICT risk management framework. This framework is designed to help financial entities identify, assess, monitor, and mitigate risks associated with their digital operations. The framework must integrate seamlessly with the organization’s overall risk management strategy and ensure that risk assessments are conducted periodically and after significant changes to the ICT environment.

Operational Impacts and Compliance Challenges

Implementing a compliant ICT risk management framework presents various operational impacts and compliance challenges. Entities may face difficulties in aligning existing risk management processes with the nuanced requirements of DORA, particularly regarding documentation practices, incident reporting timelines, and continuous risk evaluation mechanisms. Understanding what constitutes an “ICT risk” and how it varies across different business models and technologies can also complicate compliance efforts.

Regulatory Expectations and Common Implementation Gaps

DORA establishes clear regulatory expectations around the development of policies and procedures that are consistently enforced. However, common gaps in implementation include insufficient incident reporting protocols, inadequate third-party risk assessments, and lack of alignment between risk management and business continuity processes. Moreover, many entities underestimate the resources required to establish and maintain a compliant ICT risk management framework, which can lead to escalated costs and operational disruptions.

Practical Compliance Section

Concrete Steps Financial Entities Must Take

To align with DORA’s requirements, financial entities should consider the following steps:

  1. Conduct a Full Risk Assessment: Evaluate current practices against DORA’s requirements to identify gaps and areas for improvement.

  2. Develop Comprehensive Policies: Create and maintain policies that address all aspects of ICT risk management, incident response, and reporting.

  3. Implement Strong Governance Structures: Establish clear governance structures that define roles and responsibilities for risk management, ensuring accountability within the organization.

  4. Engage Third Parties Wisely: Perform thorough due diligence and assessments of third-party ICT service providers; ensure contractual arrangements include provisions that address ICT risks.

Required Policies, Procedures, and Control Frameworks

Financial entities must cultivate robust policies and procedures that govern the following areas:

  • Incident classification and reporting processes: Timelines and mechanisms for reporting incidents to supervisors.
  • Testing programs: Scheduling and executing resilience testing to assess the effectiveness of various ICT controls.
  • Continuity and contingency planning: Developing plans that allow for rapid recovery from significant disruptions.

Evidence and Documentation Expected During Audits or Inspections

During audits or inspections, entities will need to demonstrate compliance through comprehensive documentation, which may include:

  • Risk assessment reports
  • Records of ICT incidents and responses
  • Testing results for operational resilience
  • Third-party risk management documentation

Attention to detail in maintaining these records is crucial, as regulatory bodies will expect verifiable evidence of compliance efforts.

Best Practices to Demonstrate Ongoing DORA Compliance

  1. Regular Training and Awareness Programs: Ensure employees understand their roles in maintaining operational resilience and compliance with DORA’s requirements.

  2. Continuous Monitoring and Review: Establish mechanisms for ongoing assessment and adaptation of ICT risk management practices in response to evolving threats and regulatory changes.

  3. Engagement with Stakeholders: Facilitate regular communication with stakeholders, including board members, to foster a culture of resilience within the organization.

Conclusion

The EU Digital Operational Resilience Act (DORA) sets forth a rigorous framework that financial entities must navigate to ensure compliance and enhance operational resilience. As organizations work to implement the necessary policies and controls, they must adopt a structured and continuous approach to managing ICT risks effectively. By prioritizing operational resilience and addressing compliance challenges proactively, entities not only safeguard their operations but also contribute to the overall stability of the financial system. Maintaining diligent adherence to DORA’s requirements is crucial for long-term success in an increasingly digital economy.